Detection · REDMOND
Microsoft folds SIEM and threat protection into Defender as ISOC enters preview
September 23, 2026
By Ava Okello, Detection, London
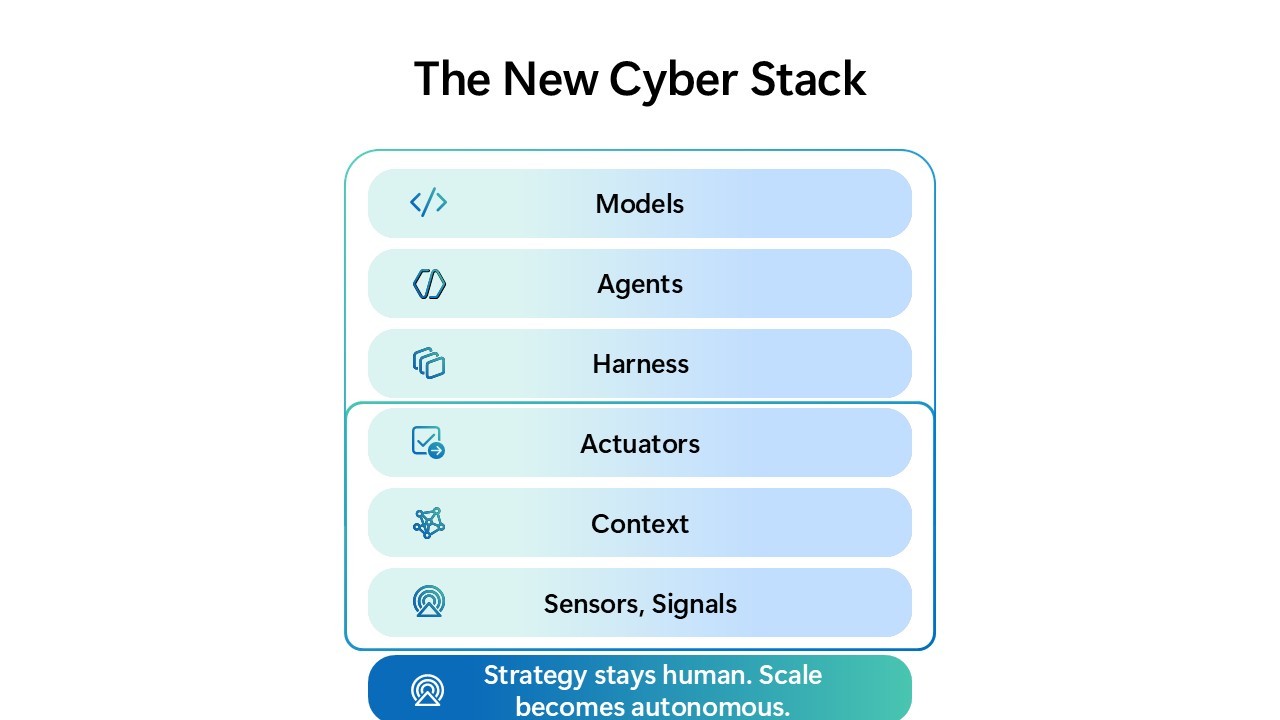
REDMOND - Microsoft on September 23, 2026, announced Integrated Security Operations Center, or ISOC, in Microsoft Defender, a preview foundation that puts SIEM and native threat protection on one shared platform so analysts and agents can investigate and act without stitching separate stacks. Rob Lefferts (Microsoft Security Blog) said agent-driven attacks raise the cost of handoffs between detection and protection. ISOC is the operations layer of Microsoft's agentic stack begun in July 2026 with Project Perception; agents supply speed while people set priorities. Microsoft points to Attack Disruption as a protection loop using telemetry, exposure insights, and threat intelligence. ISOC is a Defender preview, not a vendor-neutral SIEM.
Source: https://www.microsoft.com/en-us/security/blog/2026/09/23/reimagining-the-soc-for-the-agentic-era-in-microsoft-defender/
- Primary https://www.microsoft.com/en-us/security/blog/2026/09/23/reimagining-the-soc-for-the-agentic-era-in-microsoft-defender/
- Video https://www.youtube.com/watch?v=CCEh2debXwk
- Whitepaper https://info.microsoft.com/ww-landing-agentic-soc-continuous-defense.html
Ava Okello covers detection engineering and alert operations for SOCtember from London.